01 / DNS
Network request checks
DNS protection can restrict communication with unwanted domains based on policies and available data.


Layered protection for small and medium-sized businesses in one console. Heimdal supplies the product; APPSEC helps select modules, demonstrates the solution and deploys and supports it according to the proposal.
DNS filters connections, patching fixes known issues and PAM limits privileges. Modules are selected according to risks and licensing.
 HEIMDAL / SMALL AND MEDIUM BUSINESSES
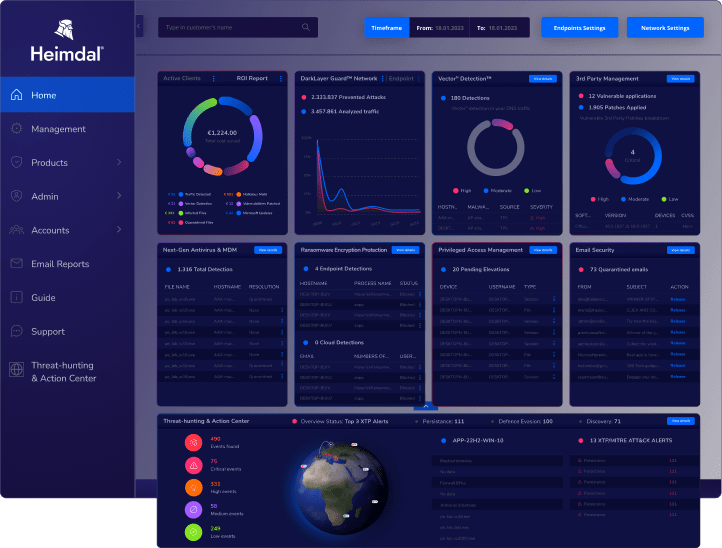
Heimdal / layered controls
Layers complement each other, but none provides absolute protection. Outcomes depend on configuration and operation.
01 / DNS
DNS protection can restrict communication with unwanted domains based on policies and available data.
02 / Email
Email filtering and analysis help reduce exposure to malicious attachments and links.
03 / Updates
Software visibility and managed updates shorten the gap between patch availability and deployment.
04 / Permissions
Least privilege and controlled elevation limit what users and processes can do.
Heimdal covers prevention, detection, access management and response. Its modules address areas such as DNS, endpoints, email, patching, privileged access and remote management.
We define the scope according to your needs and selected licences. You can start with one specific problem and add modules later.
DNS, email, patching and other layers that limit attack paths according to the selected modules.
Endpoint telemetry, context and response tools according to configuration.
Privileged access, remote management and everyday operational procedures.
We first review risks and your team's capacity. We then recommend modules, demonstrate the solution and, as agreed, prepare a pilot, deployment, policies and handover.
Detailed technical information, integrations and video guides are available on our dedicated heimdalxdr.cz website.
Commercial and technical consultation, design, deployment and support within the confirmed scope.
The product and its modules. Any vendor-provided MXDR service is separate from APPSEC support.
Environment information, pilot group selection, policy approval and everyday operational decisions.
Each module addresses a different attack path. Choose the area matching your nearest risk and discover how it works and how we can help.
Indicative qualitative view: 3 primary role, 2 additional protection, 1 context, 0 no direct role. Actual scope depends on licensing and configuration.
| Module | Devices | Users and access | Network and DNS | Updates and applications | |
|---|---|---|---|---|---|
| Next-Gen Antivirus & Firewall | Devices: primary role | Users and access: additional protection | Email: no direct role | Network and DNS: context | Updates and applications: no direct role |
| DNS Security | Devices: additional protection | Users and access: no direct role | Email: context | Network and DNS: primary role | Updates and applications: context |
| Patch & Asset Management | Devices: additional protection | Users and access: no direct role | Email: no direct role | Network and DNS: no direct role | Updates and applications: primary role |
| Ransomware Encryption Protection | Devices: primary role | Users and access: context | Email: no direct role | Network and DNS: no direct role | Updates and applications: no direct role |
| Privileged Access Management | Devices: additional protection | Users and access: primary role | Email: no direct role | Network and DNS: no direct role | Updates and applications: context |
| Application Control | Devices: primary role | Users and access: context | Email: no direct role | Network and DNS: no direct role | Updates and applications: primary role |
| Email Security | Devices: no direct role | Users and access: additional protection | Email: primary role | Network and DNS: context | Updates and applications: no direct role |
| XDR and Threat-hunting & Action Center | Devices: primary role | Users and access: additional protection | Email: additional protection | Network and DNS: additional protection | Updates and applications: context |
No. We prepare the proposal around your selected modules and needs. We verify licensing terms when designing the solution.
On heimdalxdr.cz: individual protection areas, integrations, technical requirements and video guides.
No. Standard support and managed monitoring are different services. We always describe their availability and responsibilities in the proposal.

You do not need to know whether you need a test, a technology or a consultation. We will suggest a suitable next step based on your situation.