01 / Process
Start with observable activity
A process, its parent and its actions provide the starting point for event assessment.


Endpoint prevention, detection and response for enterprise environments. SentinelOne supplies the product; APPSEC helps define scope, assists with deployment and provides support according to the proposal.
SentinelOne can connect the context and isolate a device. Response scope depends on licensing and configuration.
 SENTINELONE / ENTERPRISE
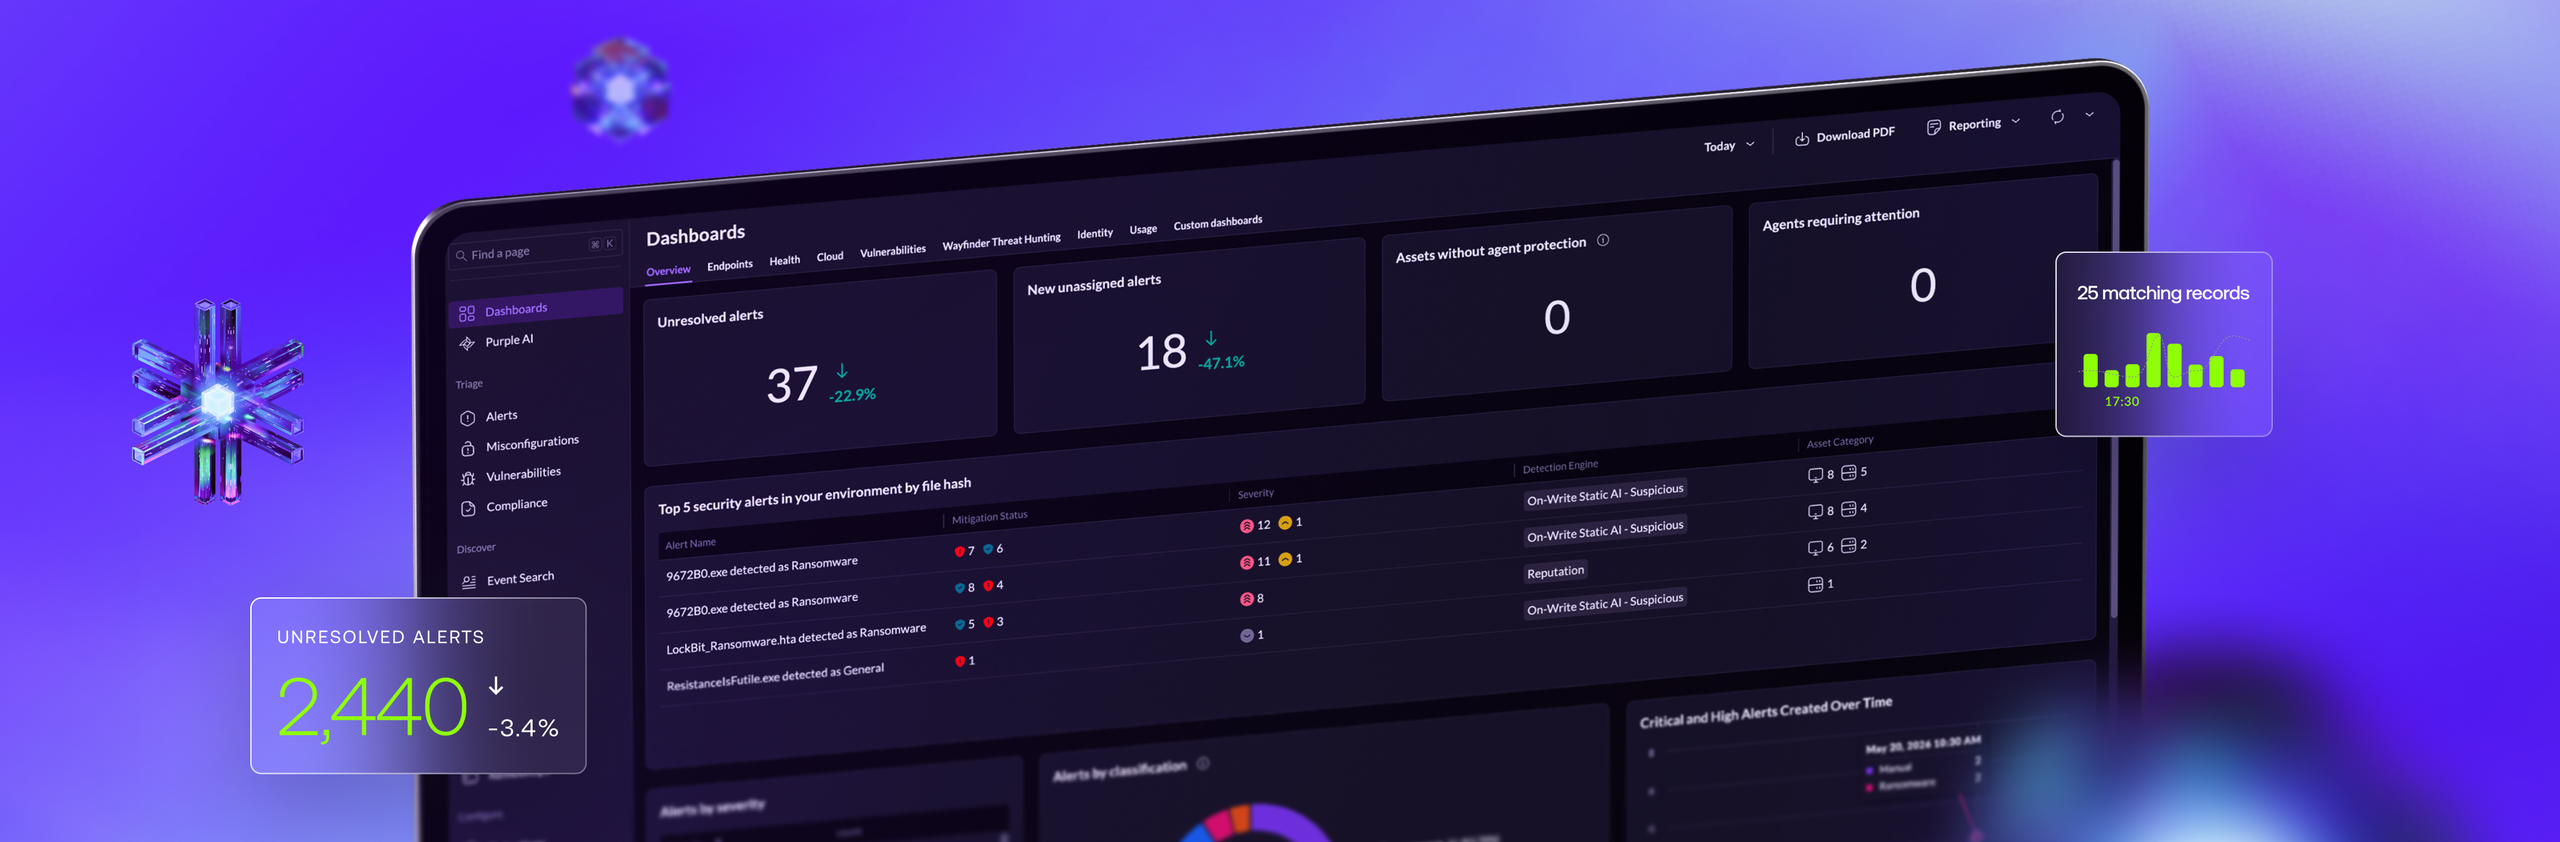
SentinelOne / event context
The diagram shows how a security event is handled. It does not promise automatic prevention of every threat.
01 / Process
A process, its parent and its actions provide the starting point for event assessment.
02 / Detection
Detection is a signal to assess. A label alone does not establish incident scope.
03 / Isolation
Endpoint isolation can limit spread when available, approved and appropriate.
04 / Context
Timelines, identities and related processes inform next steps and verify response outcomes.
SentinelOne Singularity is an endpoint protection platform that can cover other areas depending on the selected solution. At the endpoint, it combines prevention, suspicious behaviour detection, event context and response capabilities.
Available features depend on the licence package, operating system, configuration and deployment. The proposal therefore distinguishes included features, optional capabilities and responsibilities that remain with your team.
Installing an agent does not determine who will assess an alert, approve an intervention or manage recovery. Before deployment, we therefore review operational responsibilities and escalation paths together.
Endpoint protection does not replace backups, multi-factor authentication, updates, secure configuration or incident procedures. Proper deployment complements them.
Needs assessment, scoping, deployment assistance and support within the proposal's scope.
The product, licensing model, documentation and product escalation under the vendor's terms.
Access to the environment, approval of policies, technical cooperation and decisions that cannot be delegated to a supplier.
Devices, operating systems, current antivirus, critical applications and IT capacity.
We verify suitability and configuration on a selected group of devices against agreed criteria.
A phased migration, policies, permissions, escalation rules and handover to your administrators.
Channels, scope and responsibilities are clearly defined in the contract. We do not automatically promise round-the-clock availability.
Each module addresses a different part of an attack and has its own licensing terms. Discover what it does, how it works in practice, who it is for and what to check before buying.
Levels are qualitative: 3 primary role, 2 additional protection, 1 context, 0 no direct role. Actual coverage depends on licensing, platform and deployment.
| Module | Endpoints | Servers and cloud | Identities | Network | Data and logs | AI usage |
|---|---|---|---|---|---|---|
| Singularity Endpoint | Endpoints: primary role | Servers and cloud: additional protection | Identities: context | Network: context | Data and logs: context | AI usage: no direct role |
| Singularity Cloud Security | Endpoints: no direct role | Servers and cloud: primary role | Identities: context | Network: no direct role | Data and logs: context | AI usage: no direct role |
| Singularity Identity | Endpoints: additional protection | Servers and cloud: context | Identities: primary role | Network: context | Data and logs: no direct role | AI usage: no direct role |
| Singularity Network Discovery | Endpoints: additional protection | Servers and cloud: context | Identities: no direct role | Network: primary role | Data and logs: no direct role | AI usage: no direct role |
| Singularity Mobile | Endpoints: primary role | Servers and cloud: no direct role | Identities: context | Network: context | Data and logs: no direct role | AI usage: no direct role |
| Singularity AI SIEM | Endpoints: context | Servers and cloud: context | Identities: context | Network: additional protection | Data and logs: primary role | AI usage: no direct role |
| Purple AI | Endpoints: context | Servers and cloud: context | Identities: context | Network: context | Data and logs: primary role | AI usage: no direct role |
| Prompt Security | Endpoints: no direct role | Servers and cloud: no direct role | Identities: no direct role | Network: no direct role | Data and logs: context | AI usage: primary role |
| Wayfinder MDR | Endpoints: additional protection | Servers and cloud: additional protection | Identities: additional protection | Network: context | Data and logs: context | AI usage: no direct role |
Not automatically. The product, APPSEC support and any managed service are separate proposal items. Availability and responsibilities are always stated in the contract.
We first assess compatibility and risks. A pilot and phased migration verify policies and operations before protection is extended to more devices.
Primarily the numbers and types of endpoints and servers, operating systems, required scope, licence duration and the expected level of deployment assistance and support.

You do not need to know whether you need a test, a technology or a consultation. We will suggest a suitable next step based on your situation.